
Create an API key
Only team members with the Owner or Admin role can create an API key in your organization.
Choosing the right scope
Project-scoped API keys
Project-scoped API keys are limited to a single project and are designed for setups where projects must remain clearly separated. They work best for agencies and larger organizations, where each project is owned by a different team.- Access is restricted to one specific project
- Cannot create or manage other projects
- Cannot manage integrations and organization-wide alert rules, which belong to the whole organization
- No additional project headers are required when making API requests
Organization-scoped API keys
Organization-scoped API keys provide access across all projects in an organization and allow full project management. They are well suited for small teams, startups, and infrastructure provisioning.- Access to all projects in the organization
- Can create and manage projects
- Requires a project selection header on most requests
Permissions
Permissions restrict what an API key can do, resource by resource. This helps apply the principle of least privilege and limits what a key can do if it is misused. Each resource can be given one of the following access levels:- None: The API key can’t access the resource.
- Read: The API key can list and get the resource.
- Write: The API key can also create, update and delete the resource. Writing always includes reading.
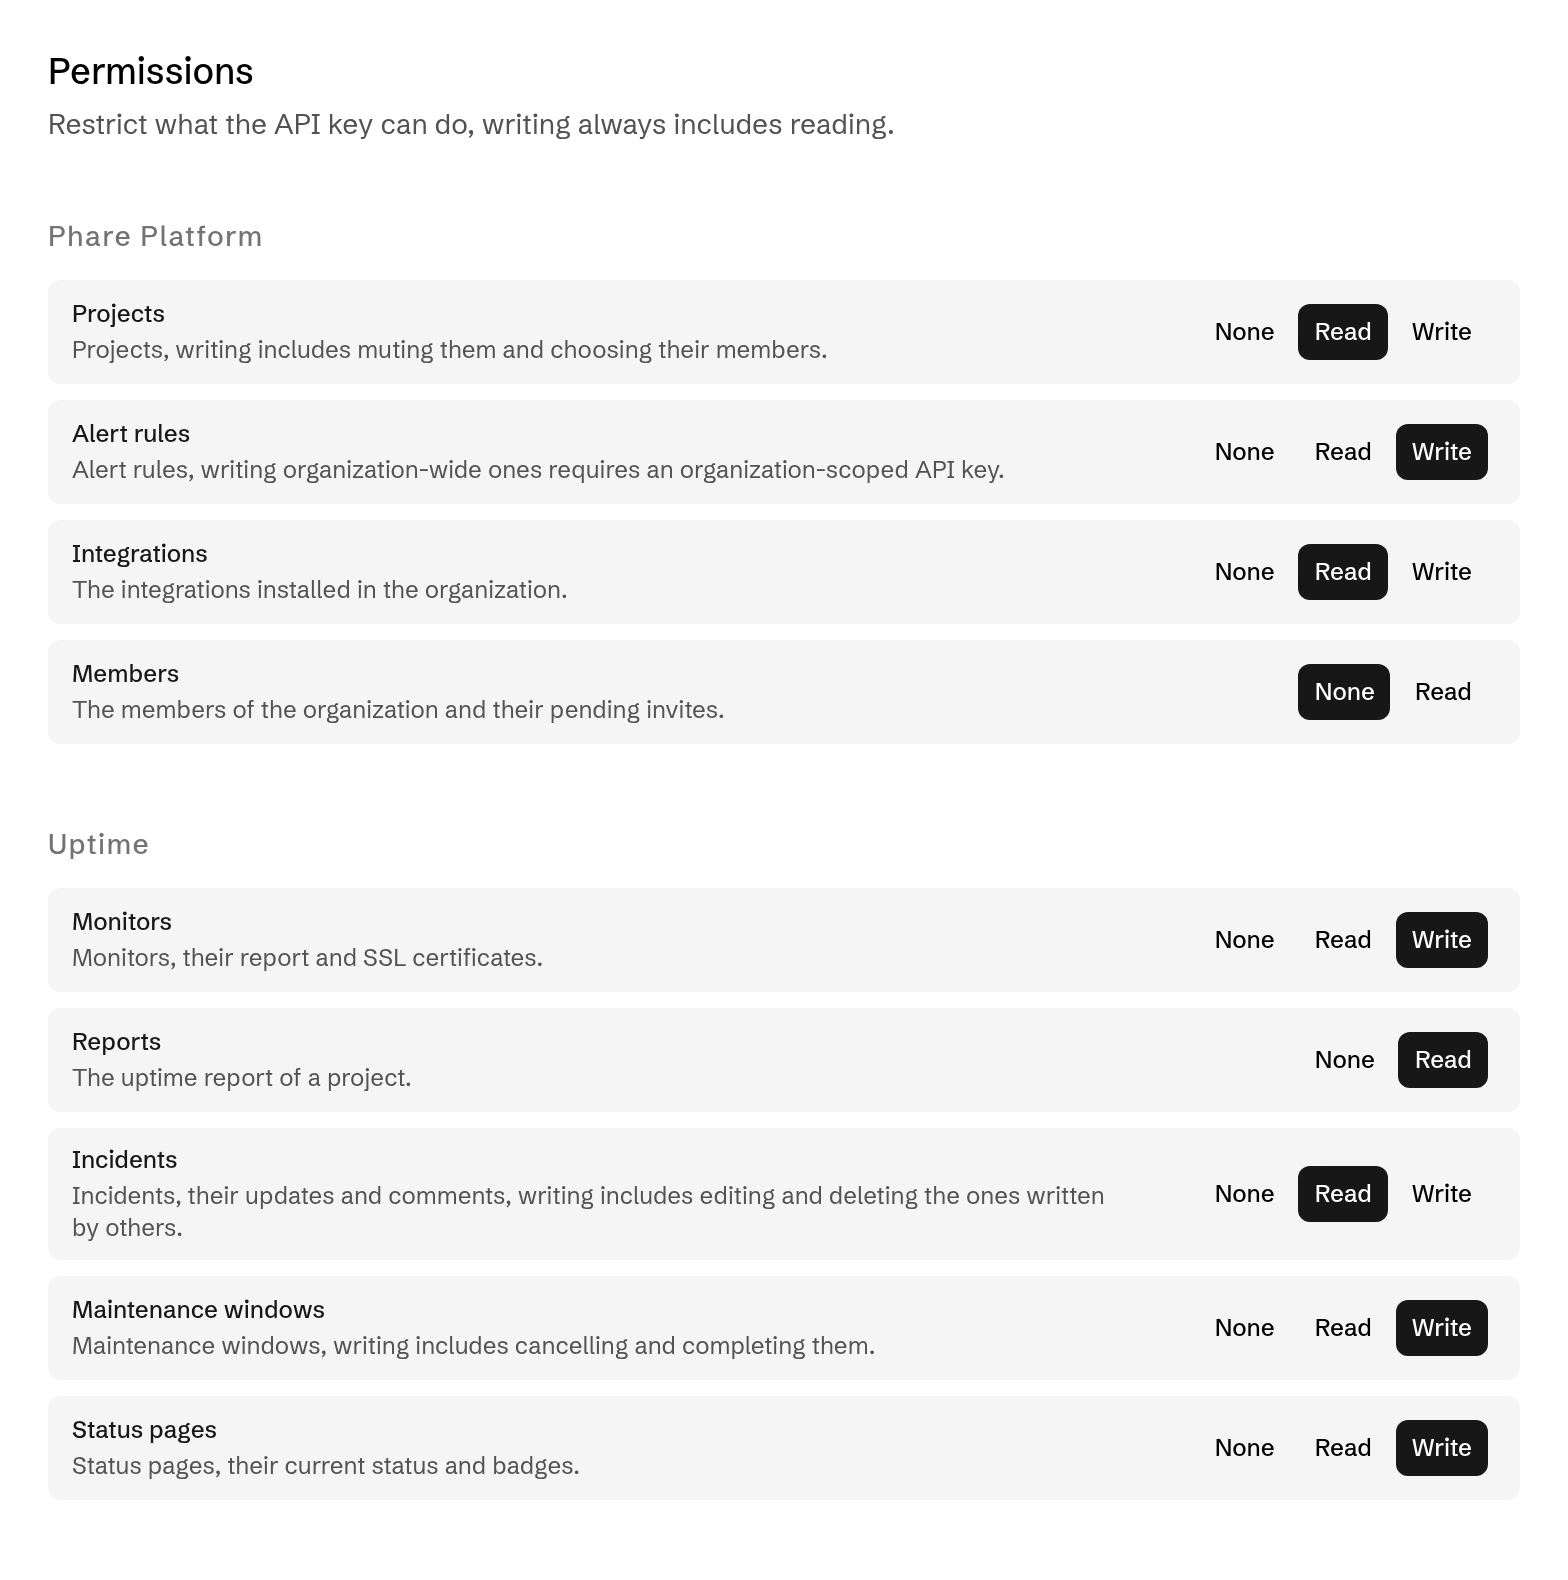
Each endpoint of this reference names the permission it requires, made of the resource and the access level, like
monitors:read or maintenance_windows:write.
When an API key is missing a permission, the API responds with a 403 status code naming the permission required:
You can create as many keys as necessary to fit your use case.
Authentication
The Phare API uses Bearer Token Authentication to secure access to its endpoints. To authenticate your requests, include the API key in the Authorization header of your HTTP requests:Project selection
If you’re using an organization-scoped API key, every endpoint except/projects most endpoints will require you to add an HTTP header to specify which project to operate on. You can specify the project by its ID or Slug:
- X-Phare-Project-Id: The project’s numeric ID
- X-Phare-Project-Slug: The project’s slug
Rate limiting
Access to the API is currently rate limited to 100 calls per minute across the organization. All API keys share the same limit. Calls made through the MCP server don’t count toward this limit, they have their own.Security
Never share your API key publicly. If you suspect that your API key has been compromised, revoke it immediately through your control panel and generate a new one.If an API endpoint is missing or a custom rate limit is needed, contact support. Phare can help find a solution that fits the use case.